my recent reads..

Atomic Accidents: A History of Nuclear Meltdowns and Disasters; From the Ozark Mountains to Fukushima
Power Sources and Supplies: World Class Designs
Red Storm Rising
Locked On
Analog Circuits Cookbook
The Teeth Of The Tiger
Sharpe's Gold
Without Remorse
Practical Oscillator Handbook
Red Rabbit

Wednesday, August 27, 2008

Reflections on a learning model

The conscious competence learning model has uncertain origins, but is probably the best known model for learning. Maybe that's because it is so simple and intuitive - I suspect making it exactly the right kind of 'model' to be picked up by the business book and management consulting fraternity.

It seems to me best applied to the development of "skills" (like riding a bike or programming in python), and less so to changing bahaviour or habits (like giving up smoking).

But for skills it works really well, and the simple 2x2 matrix of conscious-competence yields lots of interesting observations to ponder.


That's my version of the matrix. I re-label the "conscious" axis as either "self-conscious" (as in you are painfully aware that you can't do something), or "automatic" (where you have reached the stage where performance is reflexive).

Where you start, where you get to, and the path you take are really dependent on the situation and the individual. In the picture above, I've indicated a starting point of where you are self-conscious about the fact you can't do something; although the literature talks about the strict theoretical starting point of being totally unaware you can't do something (automatic - cannot do in the diagram).

So anything interesting to note?
  • Progressing from knowing you can't do something to thinking you can (the redish line above) is, I think, a perfect defintion of what we call "blur like sotong" in Singapore

  • How straight-line your pregession towards automatic-can do is probably a good guide of "natural ability"

  • Learning (or training, education and guided practice) tends to shift you up the scale of competence only - since it is more about giving you the knowledge and techniques to do the job 'right'

  • Experience (or practice with reflection) tends to move you up the conscious scale towards the point where it is automatic.


So is this model of any practical use? As a point of reflection on your own, or your collegues situation, I think it can be a good but crude diagnostic. It makes you remember things like just plain training needs to be coupled with real experience to get you all the way up the curve.

Tuesday, July 29, 2008

Heroku - Ruby in the Sky with Diamonds

I've been using Heroku since I heard about it on the Ruby on Rails podcast. It offers a hosted Rails development environment (all web-based), with instant deployment ... essentially you are running your dev, test and production environments 'in the cloud'. Heroku themselves use Amazon S3 I think.

It's worth checking out, even if you are not specifically interested in rails. A great example of how to operate 'up in the clouds'.

A couple of key things I've learned/noted in working with heroku..

Disabling the heroku toolbar


You probably don't want the heroku toolbar appearing for public users of your application (and I found it had some issues with IE). Disabling the toolbar is done by creating a file config/heroku.yml:
toolbar_collaborators: true
toolbar_public: false
request_timeout: 10

(picked this tip up from the mailing list)

Running with Rails 2.1


Rails 2.0.2 is the default, and 2.1 support took a while to arrive. It's here now. Simply update your config/environment.rb file to specify..
RAILS_GEM_VERSION = '2.1'

Distributed Version Control


Version control using git is rolled into heroku. And if you want to develop locally, there's a heroku gem that simplifies setting up your local clone. Once git and the heroku gem are installed, a typical session goes like this:
heroku create myapp
heroku clone myapp
cd myapp
ruby script/server
[..work locally for a while..]
git add .
git commit -m "some changes made locally"
git push
[..work on the server for a while and commit..]
git pull


Postscript Aug-09: heroku have since split their services in two: herokugarden.com, which includes the online, web-based editor, and heroku.com which is intended for high-performance production deployment (with no online editing)

Monday, July 07, 2008

OpenID - the missing spice in Enterprise 2.0?

I have been playing around with OpenID recently and considering its significance. OpenID offers a "single digital identity .. you can login to all your favourite websites", and its adoption is rapidly accelerating especially since services like Yahoo and Blogger have added OpenID support to the many millions of existing user accounts.

Maybe I'm missing something here, but I am surprised by the lack of attention OpenID is getting in the enterprise context.

And when it is considered, it is often as an either/or proposition. As Nishant Kaushik writes in his excellent identity blog:
.. simple web applications with minimal needs could get away with simply supporting OpenID. But that should not be confused with not requiring a full-fledged identity services infrastructure where appropriate.
I think this is somewhat misdirected; certainly not the whole story. OpenID-enabling existing applications for an external audience is already a trivial exercise. It's a simple API, and plugins or toolkits are available for most programming environments. I think the much bigger deal is looking at OpenID from the opposite perspective - using enterprise security infrastructure to support OpenID authentication.

In my view, OpenID is key to unlocking the true potential of "Enterprise 2.0", which is what I wanted to discuss here to try and explain my thoughts and get some feedback.

It may also lead us to think more clearly about what Enterprise 2.0 really is. This is the current definition up on wikipedia:
Enterprise social software, also known as Enterprise 2.0, is a term describing social software used in "enterprise" (business) contexts..
The "social" nature of Web 2.0 tends to get the headlines, and hence by simple transference must be to basis of Enterprise 2.0. Right?

However, I'm not convinced.

Expecting Enterprise 2.0 success by simply adopting social networking features of Web 2.0 just seems a little naive. For a start, it implies and requires phenomenal change in the social and organisational fabric of a company to get off the ground, and there is no guarantee the benefits will be worth the pain of change. In many organisations it may just be too much, too soon, and fail completely.

Much as I love them, I don't even think "mashups" will be the killer app for Enterprise 2.0.

I think the key is a much more mundane aspect of Web 2.0 that gets lost in the facebook frenzy: the simple fact that users are being exposed to just so darn many useful tools in the ever increasing range of web applications (or Rich Internet Applications aka RIA).

We see unprecedented utility in the applications on offer, approaching what we expect from desktop or dedicated applications. And there is an incredibly low barrier to participation - you can sign-up within a minute and with usually no immediate associated cost.

So my main proposition is that the quick win for Enterprise 2.0 is for companies exploit the RIA boom. Spend your time figuring out how to exploit the burgeoning Web Application offerings. Do NOT waste your time scheming how to clamp down on usage, or on replicating the tools yourself.

The real and immediate benefits include reduced IT spend, better utility and happier users .. and set the stage for moving to the world of "Advanced Enterprise 2.0" with mashups and social networking for example.

The caveat of course is that the enterprise must ensure that matters of availability, data protection, confidentiality and privacy are not compromised in making such a move.

But this presents a dilemma for the enterprise. A tough choice between undesirable outcomes:
  1. ban and fore-go the benefits of adopting external Web Applications for enterprise use;

  2. allow their use, but lose control of the data, identities and secondary use derived from using such applications;

  3. or be faced with re-implementing all those cool features within the firewall (and risk becoming disconnected from the external audience).


This leads us to the present state-of-the-art in Enterprise 2.0, which must necessarily work around the constraints of the corporate boundary.

  • Some companies are adopting External Web Applications where they address a largely external audience (a good example is the official Oracle Wiki which runs on wetpaint). But here they remain disconnected from internal systems.

  • For internal adoption of Web 2.0 technology, IT departments are often re-implementing all the cool stuff inside the firewall.

    The CEO wants a blog? Customer support want to setup a wiki? Sure, we can install it. Where install means friggin' around for a few months to select and acquire the software, integrate it with the standard enterprise security/monitoring/hosting/blah environment, customise it to the corporate branding etc etc.
Toto, I've a feeling we're not in Kansas any more.. suddenly Enterprise 2.0 doesn't seem so exciting.

And I think it denies the dirty little secret that I bet exists in most organisation: your employees are already using these services for business purposes!

Using a personal credential for business purposes on an external service (whether OpenID or not) presents a whole range of challenges:

  • It is a provisioning nightmare. What happens when the employee leaves? The company doesn't control the account, so it can't be disabled. Whether you can remove access from any corporate data held in the external service depends totally on the application itself and how it was setup.

  • For the individual, there is a concern about keeping their professional and private lives appropriately separated. Too easy for your tweets to end up in the wrong hands in the wrong context.

So what's a girl to do? I'd suggest the answer is pretty obvious - we need corporate identities that can extend beyond the boundaries of the the organisation in a safe and controlled manner. This was the intention with SAML, but adoption has been slow - I suspect hindered by the complexity of its WS-Deathstar burden - and now OpenID is streets ahead in terms of acceptance (an interesting parallel to the adoption of SOAP v. REST for SOA Web Services).

In other words, the key to all of this IDENTITY.

Imagine for a moment the ideal world. I would have a corporate identity that works transparently within the enterprise and also for useful external services. And I could keep this quite separate from my personal identity (even though I may use some of the same external services on my own time).


The question now is whether we are far from being able to achieve this? I think not...

The call to Enterprise Identity Management Stack providers..

That means Microsoft, Oracle, IBM, Sun and so on.. the companies that produce the security software that is managing your enterprise identity every time you sign in to an enterprise application.

Many of these guys are members of the OpenID Foundation, but on the whole it is hard to find clear statements of direction at the moment, and the initial focus has been around demonstrations of how they can use credentials from other OpenID providers.

We need to see two things in particular:
  • OpenID provider support in their core identity management stacks, so that enterprise credentials can be used as OpenID credentials under the control of the company (e.g. they can be disabled when the employee leaves). Call that part of a "Service Oriented Security" strategy if you like, just make the option available;-)

  • Include that ability to blacklist/whitelist sites that the credentials can be used for.

    There will always be good reasons why certain Web Applications may be off limits for corporate use. For example, a law firm may not be able to use Google Documents because of jurisdictional concerns.


Dion Hinchcliffe presented the case well in the recent article "openid: The once and future enterprise Single Sign-On?", along with a great visualisation:


The call to Web Application providers..

Firstly, the big guys like Yahoo! need to support third party OpenID credentials. This seemed to be the main thrust of Hinchcliffe's article. I hope this is just a matter of maturity and not business model pig-headedness, but to offer OpenID sign-in only if your OpenID provider is the same company is not really in the right spirit of things!

More generally applicable however is a major consideration for any Web Application provider that wants to target the enterprise market: addressing the security issue with OpenID support only opens the door. To step through, you must be ready to meet the specific demands of an enterprise customer.

First of these must be data ownership. I didn't want to focus on it in this post because I think it is an orthogonal concern to security. But if you want enterprise customers, be prepared to to consider requirements such as:
  • Access to all data owned by the company's users on the service. For backup, export, and analytics.

  • Audit and compliance

  • Service levels

The call to Enterprise Software vendors..

The idea of a "Web 2.0 appliance" is I think very attractive to many organisations: an easy on-ramp to the space without the need to build up a whole range of specialist skills within the company. In the appliance category I would include Oracle WebCenter and the new IBM Mashup Center. Needing OpenID authentication support in these products is of course a no-brainer in order for them to have appeal in cases where you wish to mix internal and external user audiences.

Enterprise Software vendors need to go further however. The enterprise of the future, which expects to operate seamlessly on the web, will need the ability to "export" corporate identity to the world. Right now, that means capabilities like having OpenID provider support in your Enterprise Identity Management services.

Given the state of consolidation in the industry however, OpenID may present a dilemma for vendors who are faced with the prospect of OpenID support in their Identity Management stack cannibalizing sales of their application suites, as users start to exploit external Web Applications.

But to be recalcitrant and stand against the move to OpenID will only accelerate the onset of a winner-takes-all showdown in the enterprise applications market.

Personally, I believe the showdown is inevitable: with the combined pressures of RIAs, cloud computing, oligopolistic pricing and increasingly sophisticated open source alternatives, I think it is quite likely we will see the enterprise software market go supernova within the next 5 years i.e. blow itself to pieces after a few more years of consolidation ... but that's a topic for another post perhaps;-)


The enteprise software vendors that survive will be the ones who truly embrace being open, and that includes OpenID.

Conclusions?

Well, I wonder if I've convinced anyone?

To me it seems that the ability for enterprises to add OpenID provider support to their security infrastructure will be the key to unlocking the full potential of Enterprise 2.0.

Until such a facility is available from the mainstream Identity Management vendors, we will just be messing around on the fringe.

NB: edited for clarity 9-Sep-2008

Tuesday, June 24, 2008

Regrettably .. my Disqus experiment is over

It held great promise .. and I think still does .. but I am calling my experiment with Disqus commenting to en end.

I've unfortunately had too much feedback that it is just too (friggin) hard for the casual commenter. Bash me upside down, isn't it?

I hope the Disqus folks to manage to improve the interface to remove any barriers to adoption, because I still do look forward to the day we can wave goodbye to forums, and bring in an era of universally connected discussions!

Monday, June 23, 2008

The cutting edge of web applications? 280slides

It is amazing to see the art of the rich internet application (RIA) rocketing ahead over the past year or so, after a slow and troubled gestation over the past 12 years or so. Much of the progress has been incremental and focused on technical reimplementation of old non-web concepts (think event handling in a form GUI). Sometimes we take a big leap forward (think rails, prototype).

37signals arguably kicked of the current phase of web applications with basecamp that finally allow us to forget we are working in a browser (or was it writely? - now google docs).

Now we are seeing a selection of frameworks or products specifically designed for building modern RIAs. Rails is of course now fairly established in this space, but products like Flex, Air, Appcelerator and WaveMaker are redefining the envelope.

Well I'll be bold enough to say now that I think the guys from 280North have just redefined the cutting edge again with their powerpoint/keynote killer called 280Slides.

It's just out in public beta (isn't everything?), but I challenge you not to be impressed with just how much like a great piece of desktop software it is ... except you've also got the power of web access, sharing and delivery.


Perhaps even more impressive is the story behind the app, which you can hear in an interview on net@nite #57. When these guys set out to write web applications (like 280slides), they wanted a real development environment - like cocoa which they were familiar with having worked at Apple. So they built a cocoa-compatible/Objective-C like platform that runs in pure javascript. That's what is running 280slides, but building it is like building any old cocoa app. NB: the platform is still being kept internal, but their intention is to go open source when it is ready for the wild.

280North have only recently gone public with 280slides and the platform they have been building. Interesting to see at the same time we have Apple announcing a more conventional javascript library SproutCore. Can anyone spell a-c-q-u-i-s-i-t-i-o-n  t-a-r-g-e-t?

Exciting times!

Tuesday, June 17, 2008

Doing one thing at a time

James Shore discussed Agile Release Planning on this recent PM podcast, and it was refreshing to hear the benefits of agile pitched to a product management audience.

Like the best ideas, the tenets of agile appear almost too simple to be true. "Master of the bleeding obvious" Basil Fawlty would say. Yet most organisations seem structurally incapable of behaving along these lines.

James' presentation is very entertaining, and well worth a listen. He keeps the agenda short and well tuned to a PM audience. Although the ideas are born from a software environment, they are largely transferable to other domains. A discussion of five concepts to help you increase the value you deliver in business:

  • Work on one project at a time .. it improves your ROI

  • Release early and often .. get to market faster with a minimum, but valuable feature-set. Not only do you get to take advantage of the real customer voice sooner, but, again, better ROI.

  • Adapt your plans .. to slavishly avoid change is to confound the opportunity to increase the value of your work as new things are learned along the way

  • Conduct experiments .. your project can have many outcomes, and you will never know which is best unless you test options, collect data, and analyse

  • Plan at the last responsible moment .. avoid costly planning that is basically trying to predict the future (unsuccessfully). The later the decision, the more information you will have available to make a good decision.

The one project at a time struck a chord with me, as I've recently been campaigning in a minor way along these lines. The classic "proof" is the positive impact it can have on ROI if you allow appropriately sized teams to focus on one thing at a time. This is of course in addition to any productivity benefits you get from avoiding task switching, and giving people the chance to get into a flow state.

Here's my version of the graphic to illustrate the point:

Monday, June 16, 2008

bookjetty - a great new site to track, share, buy and borrow books

I've fallen in love with bookjetty, a great new site for books by Herryanto Siatono.

Although my It's a Prata Life blog is officially dedicated to prata (and always will be!), I also use it to keep a diary of the books I'm reading. I probably always will, but I do make sure to try out all the "book tracking" sites, facebook apps and so on that I come across.

None have really jiggled my worm until I discovered bookjetty.

The killer feature for me is the great library integration on the site. It helps answer all the usual questions I have whenever I hear about a new book..

  • Have I already got it or read it before?

  • Does one of my friends have it? Maybe I can borrow it..

  • Can I get it from the local library?

  • Can I buy it online?

  • (oh, and if the last two steps fail, I may actually visit a real bookstore!)

The library catalogue checks work a treat - right within your booklist. I used this feature yesterday as I knew I would be heading to the library. Within 5 minutes on bookjetty I had added a few books I'd been interested in reading and found out that 3 of them were available and on the shelf at my local library. An hour later, I had them checked out.

The bookjetty developer(s?) have done a great job of integrating the libraries, especially considering that most are still running archaic web 0.1 systems which are not very mashup friendly. I've posted before about a kludge to do library lookups from an amazon page, but it never works very reliably because of the dumb library catalogue it needs to talk to, so I can appreciate some of the challenges they may have had.

And here's an example of how the library checks appear...


If you are into books, I heartily recommend you go and register at bookjetty and check it out!

Sunday, June 15, 2008

Moving to Disqus for Comments

I recently moved this site's commenting feature to disqus.com after listening to the great interview with Daniel from Disqus on net@night#53. I see I'm not alone..

You may think A Blog Without Comments Is Not a Blog, and most people have reviewed Disqus in terms of the improved commenting features it provides.

There is another point of view that really hit home for me as I considered the move.

I remember the pre/early web days when I was a very heavy nntp (news) user. In the job I had at the time, it became my lifeline to various specialist groups where I would share the little I knew and was able to draw on the sometimes instantaneous feedback from a global community of peers. I think those days still rank as the best and most productive community networking experience I have ever had.

As the early web came to life there were many areas in which we took short-term hits for (hopefully) long term gain. We moved from (pre-Domino) Lotus Notes to web publishing for example, not because it was better but because it represented a broadly accessible, stanadards-based platform. Web 2.0 is I think only now starting to surpass the degree of interactivity you could achieve with Notes circa 98.

IMHO, collaboration is another area that's been through a similar process. Simplifying somewhat, I saw blogs and web-based forums as a bifurcation of the old collaboration experience I had with nntp. Blogs at least did a decent job of allowing anyone to publish what they thought was worth sharing. Web-based forums never really tickled my mustard however.

Implementations have never been quite as efficient for greasing collaboration as nntp, and they lack the universal federation model that nntp has always had baked in. It also meant that forum discussions and information publishing (via blogs etc) became divorced.


So when I look at Disqus (and other similar offerings), I see a scheme to finally re-unify the publishing and discussion worlds. Disqus provides the forum capability integrastes with tyhe blog publishing world, eliminating the question "should I blog it, post it to a forum, or both?"

As you can tell from my little diagram above, I don't see much role for web forums as we know them today in the new world of collaboration. Maybe I am overly negative, but it does make me smile/cringe whenever I hear someone talking about "web 2.0: you know, forums etc..."

Notes on integrating Disqus with blogger


I'm using blogger. Since there are various guides around for the manual integration of Disqus, I thought it would be worthwhile to report on how the process went for me.

I'm using customised blogger layouts for my blogs, and actually found that the automatic integration support built into the setup process on Disqus worked very well.

Just a few things to note:

  • I used the "upload template" feature to load the version modified for me by Disqus. I think because of this, I had to "expand widget templates" and save the template again after the upload to have it take effect.

  • There is no import of existing comments yet (future feature), but it is possible to go back to old posts that do not yet have comments and switch them to Disqus mode by selecting the "Don't allow" reader comments post option.

Postscript: as I noted here, I've unfortunately had to drop my disqus experiment because it just isn't proving easy enough for people to use. Shame .. for now!

Some more on secure social networking - iHazYrCreds

The other day I added my voice to the call to end the perfidious practice of social networking sites requesting your email password.

In the discussion I made an off-hand reference to a fictitious site called iHazYrCreds. Well, it's not fictitious any longer ;-) For better or worse, you can now visit iHazYrCreds.tardate.com to find out more about the common password traps to avoid.

I'd like to see the day when asking for an email password in order to "import contacts" is deemed totally unacceptable (and negligent professional practice).

I would also welcome any moves by the big email providers (google, yahoo etc) to explicitly outlaw such use in their terms of service. I'm no lawyer, but I believe it is debatable whether it is already a violation.

net.gain


..or "how to (try) and make the new economy work like the old one"

I recently borrowed John Hagel III and Arther G. Armstrong's Net Gain: Expanding Markets Through Virtual Communitiesfrom a colleague for a quick read.

It was published in 1997 by McKinsey & Company, and I must say it kinda shows. The book suffers from a myopic pre-occupation with the dual assumptions that:

  • organisations must race to establish virtual communities: the spoils will go to the fast and the bold
  • the aim is to profit from transactions conducted by the community while also garnering peerless customer loyalty

Ah, the golden days of the internet bubble! This is an interesting read if for no other reason than to see how far we have come; how much has been learnt, and how much we have yet to learn.


As I studied the authors' recipe for profitable community-building I found myself challenging the principle that success requires an imposition of control by an organisation: the company studies the market, decides what community should be built, writes a business case for it, and appoints the expert team to design, build, launch, and market the community.

This is an astonishing proposition given the book's initial premise:
The rise of virtual communities .. has set in motion an unprecedented shift in power from vendors of goods and services to the customers who buy them.

"Over my dead body!" I can hear the voices echoing from the boardroom - undoubtedly the prime audience for this book, which I think could reasonably be subtitled "how to (try) and make the new economy work like the old one".

The idea of a "community" that is both external to the organisation while remaining under its control permeates the book, and is perhaps the primary misconception that has taken the past 10 years to rethink and recognise for the oxymoron that it is.

This is closely related to the fundamental yet unspoken assumption of a hard boundary between the corporation and the customer/community. In parts of the book that consider the use of communities within the corporation, the emphasis is very much on within the corporation, or at most, between business partners.

My comments have been a little disparaging, and it is perhaps unfair to find fault in failing to predict the future accurately. It does mean that this book is now little more than a historical curiosity.

However, the book I would be very interested to read is a "10th anniversary rewrite". For my money, I'd say that's Wikinomics: How Mass Collaboration Changes Everything (any other recommendations? I'm keen to hear..)

For now, I think I'll let Geek and Poke have the last word...

Geek and Poke


Originally posted on It's a Prata Life

Friday, June 06, 2008

'Promote Bad Security Practice' Grand Achievement Awards

As usual, Jeff cuts to the heart of the matter on Coding Horror when calling out Yelp for the astonishingly evil and unconscionable act of asking users to hand over their email passwords.

I am not sure who started this, but it has somehow scarily become accepted practice, especially among the social networking sites. Facebook, LinkedIn, Plaxo ... they all do it, and seem to think that waving some privacy mumbo-jumbo 'but you can trust US!' makes it OK. Some are particularly heinous, like Tagged, which obscure the fact that handing over your email password is optional.


As many have pointed out (see the comments on Jeff's post), this is a lazy solution to a problem that is solvable in ways that do not need to compromise user security.

Facebook, LinkedIn - these guys should know better. And I think have an obligation to do better, especially since it is becoming more and more common for a social networking site to be an individual's first experience on the net. While the old hands may have well-ingrained security awareness thanks to the evangelizing efforts of people like Steve Gibson and Leo Laporte on the Security Now! podcast, we have a whole new generation of users being taught exactly the wrong thing thanks to the misguided and irresponsible acts of the social networking sites that are requesting email passwords to be handed over.

The proliferation of this perfidious practice must be reversed! A good first step is to heap professional scorn on anyone associated with developing such a feature. Shame!

Tuesday, June 03, 2008

Oracle Release Timeline with Dipity

Derek Dukes was on net@nite #53 the other week, and it was really interesting to hear him talk about dipity.

Dipity is an experiment in information organisation, with time being the primary dimension currently being explored. Similar in a way to MIT's SMILE widget, which I was investigating a while back for visualizing time-based information.

Dipity shows a great deal of promise, and I like its emphasis on self-discovery and organisation information if directed (rather than everything having to be painstakingly entered). It is certainly a fun way to get lost for a few hours and learn a whole lot of stuff you never set out to study (just go to the home page and start checking out different timelines!)

Ulrich has already worked up a history of Oracle Releases. Not complete, but a fantastic visualisation that would be worth supporting and maintaining!

NB: I'm posting a static image here for now, because the embed code doesn't seem to work in all browsers at the moment.


Adding reCAPTCHA to Oracle SSO - now on sourceforge

Yes, it's time for some house cleaning!

One of my favourite little hacks is how to add reCAPTCHA to Oracle SSO, which I wrote about last year. I've now finally got around to setting it up with its own sourceforge project.

OssoRecaptcha is a demonstration of integrating the CAPTCHA service from recaptcha.org with Oracle Single-Sign-On. It can be used in production OSSO deployments, and also as an example of integrating any 3rd party authentication system with OSSO.

SourceForge.net Logo

Monday, June 02, 2008

Request header rewrites with Java servlet filters - now on sourceforge

Some time back I posted a sample and discussion of request header rewrites with Java servlet filters, and I now finally got around to setting it up with its own sourceforge project.

RewriteRequestHeaderFilter is a Java servlet filter for request header rewrites according to regex rules specified in the servlet init parameters. It is packaged as a sample application and also jar that can be inserted into any arbitrary site.

SourceForge.net Logo

Sunday, May 25, 2008

Config Files for Windows - an Enhancement

In a previous post, I described a general scheme for managing config files for Windows.

Well, there's a simple enhancement that I've added concerning how to locate the config file for the script in question.

The issue is that if I run a script, you always wanted to look for the config file relative to the script location. This can be easily done using Windows Batch Parameter Expansion. %~dp0 expands to the path of the current script, and %~n0 is the name of the script file. Hence, to name the appropriate config file for a script, we generate the name as follows:

set LOCALCONF=%~dp0conf\%~n0-%COMPUTERNAME%.cmd

Blog Stats

I want a t-shirt just like this for my birthday, except I'd change it to "..than MY blog" and add my url;-).


Originally posted on Prata Life..

Business Networking that Doesn't Suck

I really like Geoffrey Grosenbach's ruby on rails podcast, especially because it's not just about rails (even though Rails is a keen interest of mine).

On the latest issue, I was excited to learn about biznik.com. "Business Networking that Doesn't Suck" as they say.

I immediately subscribed, but was disappointed to find that there's nothing happening in my local area yet (Singapore), at least not within 6000km.


Something that we should change soon, especially given the attention paid to entrepreneurship in Singapore. Take the efforts of SPRING for example, or the investment that the government is making in Interactive Digital Media.

I love the idea of this site, and hope to find some local compatriots up there soon!

Saturday, May 24, 2008

Monday, May 19, 2008

Tu Plang, Unit and the Green Papaya


I've had Regurgitator's Tu-Plang and Unit since when I was working in Sydney around 98/99. These albums are classics. I love their sound, and the lyrics are smart. They still get a regular listen, and that's not going to stop.

In a twist, I saw recently on the Food Lover's Guide to Australia that Quan's mother established a Vietnamese restaurant in Brisbane called Green Papaya, and it has great reviews.


It was Hanoi-born Lien Yeomans's dream come true - opening her own restaurant. At Brisbane's Green Papaya she cooks dishes from North Vietnam. She says she has her rock star son Quan to thank for her fame (he’s with the band Regurgitator) but we think it’s her recipes, each one linked to a personal story from her incredible life.


So next time I'm in Brisbane...


View Larger Map

Sunday, May 18, 2008

Calendar


Day to day, our time is marked by weeks, months and years. We take it for granted that no matter where you are on earth, you always know where you are in time.

The calendar is such a routine concept that it takes a book like David Ewing Duncan's excellent and most engaging Calendar to make you stop and think.

A 7-day week is completely arbitrary for instance, apparently originating circa 700 BC in Babylon, and probably influenced by the seven known planets (at the time).

Months are confusion personified. Inspired by the lunar cycle, one is left with the dilemma of trying to fit the cycles within the solar year. The chart below (produced with the open source lcap program) is probably the easiest way to see how the lunar months drift in relation to the solar year. Some, like the Greek astronomer Metron, attempt to rationalise the relationship with great precision (the 19-year Metronic cycle has 7 years of 13 lunar months followed by 12 years of 12 lunar months. Even that is not completely accurate). To most calendarists however, months scarcely retained a notional relationship to the moon, becoming little more than convenient units of time upon which to hang the names of Gods and Emperors.


NB: the difficulty in tracking the moon also came up in relation to the challenge of measuring longitude. Accurate moon charts would have allowed mariners to determine their position even in the absence of accurate time-keeping devices. Predicting the moon's course in the end proved to be much more challenging than building a clock that could survive a nautical adventure and still keep good time. See Dava Sobel's Longitude.

The idea of the solar year - the complete cycle of the seasons from one solstice to the next - is fundamental to how we conceive the passage of time. But we don't often think about the difference between a sidereal year (time for the earth to complete one complete orbit of the sun), and the tropical year (time from one vernal [spring/March] equinox to the next). Or the fact that the year is so very slightly different if you measure between the June or December solstices or the September equinox. And then consider that the Earth is a huge object hurtling through space and subject to varying gravitational forces and other bumps and jitters.

Once you have boiled all this down, it seems a "day" is about the only fundamental unit of calendar time that makes sense. Everything else is just convention and approximation!

Considering the difficulty of measurement, and the many social, political and religious factors involved in common convention, it is quite extra-ordinary that we even have a universally accepted calendar today.

It is easy to forget just how recent a phenomenon this is, and how long its introduction was in the making.

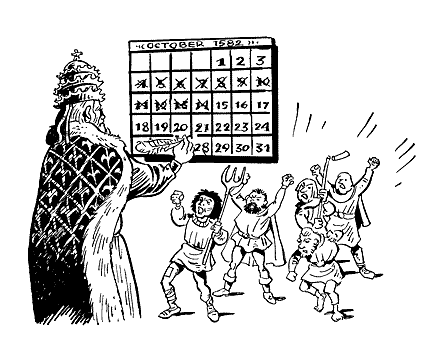
The introduction of the Gegorian calendar required 11 days to be lost for ever!The Gregorian calendar we use today was officially launched by Pope Gregory in 1582, but it wasn't introduced in Britain until 1752 with many countries not adopting it until the 20th century (for example, Russia in 1918 and Greece in 1924). Many quote Mao Zedong declaration of the People's Republic of China in October 1949, which included a point on the adoption of the Gregorian calendar, as the final triumph for a universal calendar (although many cultures still maintain parallel systems such as the Chinese lunar calendar). But do not forget that the flaws in Julius Ceasar's previous calendar had been know long before - the cause of much consternation at the Council at Nicaea in AD325 over the scheduling of Easter, and the subject of the monk Roger Bacon's most distressed entreaty to Pope Clement in 1266 to:
.. apply excellent remedies in this particular .. If then this glorious work should be performed in your Holiness' time, one of the greatest, best, and finest things ever attempted in the Church of God would be consummated.

All of this is of course the background to an epic tale that finds a thread through all peoples over all time.

Which is really the genius of David Duncan's work. He is a great explainer, and in telling the story of the calendar, he tells the story of much of human civilization. And where other "histories of the world" tend to struggle to fit a narrative thread across time and place, the story of the calendar provides Duncan with a perfect segue. The result is the most enjoyable, understandable and effective history lesson I have ever had.

If you have just the slightest interset in history or how the calendar came about as we know it, I couldn't recommend this book more highly.

Other interesting facts:

  • In Britain, New Years Day was celebrated on March 25, the Feast of the Assumption, until it was changed to January 1 in 1752. There are over 30 definitions of New Year listed on wikipedia.

  • Until the modern era of atomic clocks, the most accurate measurement of the year was by Abu Allah Mohammed Ibn Jabir al-Battani in AD 882 (22 seconds short). al-Battani's work came from the same period of Arab innovation that produced modern algebra and added "zero" to the nine Indian symbols that eventually became our familiar number system.


Calendar for December from a French Book of Hours, written around 1470:
Calendar for December from a French Book of Hours, written around 1470
Easter table, England, 1073:
Easter table, England, 1073
Originally posted on Pratalife